click-sud.pro — Romanian TV Piracy Farm,
.in APK Malware Network & Indonesian Gambling Traffic Sale
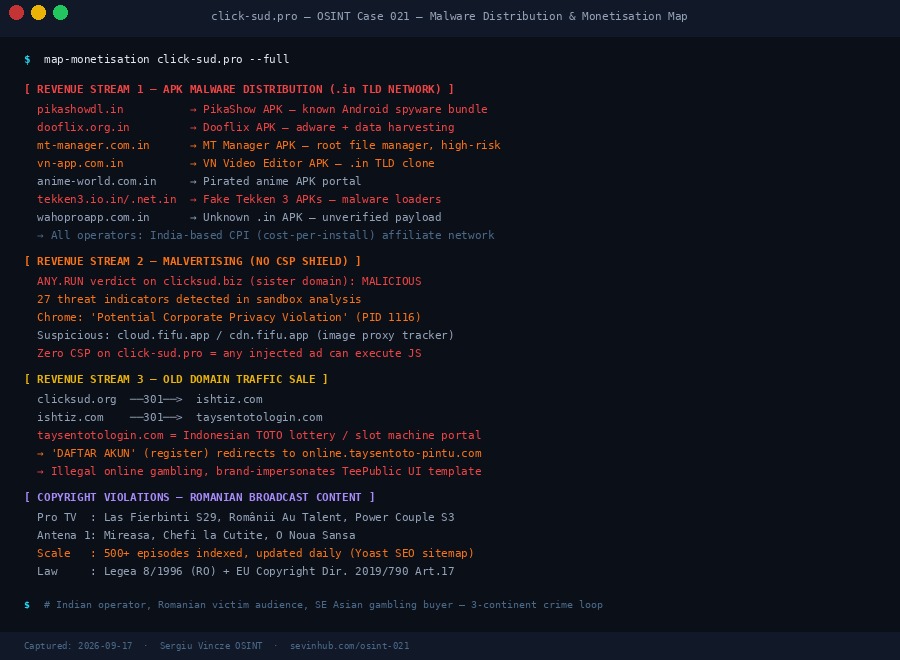
A WordPress piracy portal serving 500+ unlicensed Romanian TV episodes attracts the diaspora with free content, then monetises via a confirmed malicious ad surface (zero CSP, ANY.RUN verdict on sister domain), eight Indian-operated Android APK install-partner links, and the sale of its legacy clicksud.org domain traffic to an Indonesian illegal online gambling operation. A three-continent revenue loop built entirely on other people's content and malware delivery.
Serial Domain Cycling — Piracy Network Across 4+ Domains
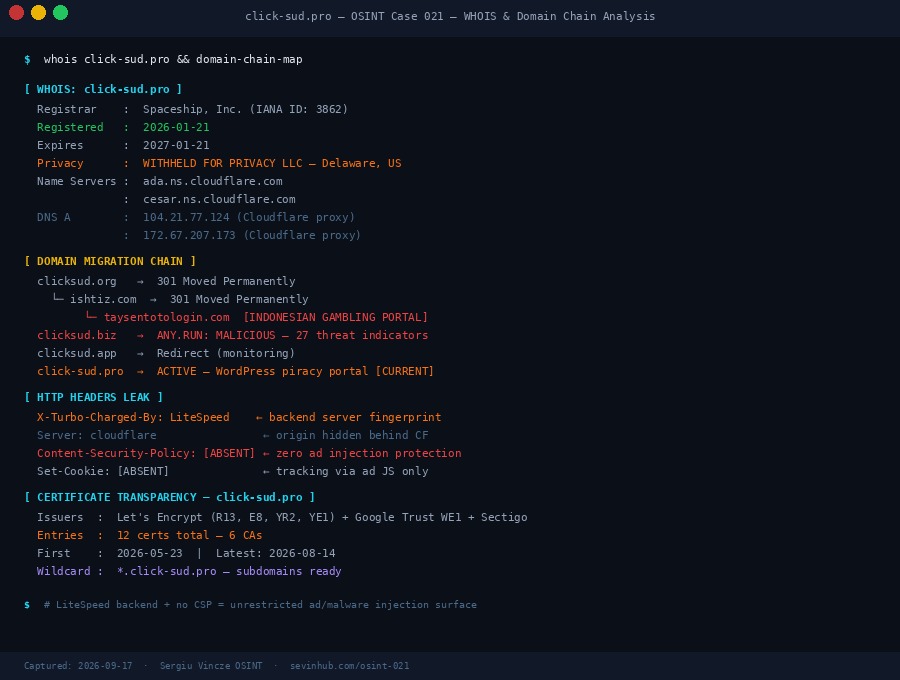
The operator runs a domain-hopping strategy to survive copyright enforcement. The original clicksud.org domain has been abandoned and now 301-redirects, cycling through intermediate hops before landing on an entirely unrelated Indonesian gambling site. The current active site is click-sud.pro, registered January 21, 2026 via Spaceship, Inc. with full identity privacy through WITHHELD FOR PRIVACY LLC (Delaware). The .pro TLD is a deliberate choice: harder to trademark-challenge than .org or .com, and Spaceship has a weaker abuse track record than larger registrars.
Sister domain clicksud.biz received a confirmed MALICIOUS verdict from ANY.RUN sandbox analysis, with 27 threat indicators and a "Potential Corporate Privacy Violation" flag from Chrome processes. This directly links the operator's broader domain network to malware behaviour, not just piracy.
LiteSpeed Backend Leak + Zero-CSP Malvertising Surface
Despite Cloudflare proxying hiding the origin IP, a passive HTTP headers check reveals the backend server type via the X-Turbo-Charged-By: LiteSpeed header. LiteSpeed Web Server is the dominant backend for Indian shared hosting providers (Hostinger IN, HostGator IN, BigRock), strongly indicating the physical origin server sits on Indian infrastructure. This aligns with the Indian-operated APK partner network in Finding 3.
Critically, the site serves no Content-Security-Policy header. With no CSP, any ad network or injected script can execute arbitrary JavaScript, load external iframes, exfiltrate cookies, or deliver drive-by malware to visitors. This is not an oversight: running piracy portals with aggressive ad networks requires CSP to be absent so ad tech can insert pop-unders, redirectors, and crypto miners without being blocked by the browser.
Android APK Malware Distribution Network — 8 Indian .in TLD Install Partners
The site's footer carries eight outbound links, all pointing to .in TLD domains hosting Android APK download pages for well-known piracy and utility apps. This is not organic linking. These are Cost Per Install (CPI) affiliate arrangements: the site operator earns $0.10–$2 per APK installed by a Romanian visitor. Each APK is a repackaged version of a legitimate app bundled with adware, spyware, or data-harvesting payloads.
PikaShow and Dooflix are well-documented malware vectors in the Android threat research community. MT Manager's .in TLD clone grants root-level file system access. The .in TLD pattern confirms a single Indian affiliate network operating all eight domains. Romanian users who download these APKs expose their devices to SMS interception, credential theft, and location tracking.
Old Domain Traffic Sold to Indonesian Illegal Gambling Operation
The original clicksud.org domain, which historically held the site's SEO authority and backlink profile, has been sold or leased to an unrelated operation. A passive HTTP follow reveals a two-hop redirect chain ending at taysentotologin.com, an Indonesian online TOTO lottery and slot machine portal. The intermediate domain ishtiz.com appears to be a traffic broker or redirect monetisation service.
The gambling site impersonates TeePublic's UI template and operates registration flows at online.taysentoto-pintu.com. It advertises "4D Lottery Generator" tools, promises large prizes and fast withdrawals, and provides no business registration or gambling licence information. Online TOTO operations of this type are illegal in most EU jurisdictions and unregistered in Indonesia. Romanian users following old bookmarks or search-engine cached links to clicksud.org now land on a gambling lure targeting them without consent.
500+ Episode WordPress SEO Farm — Unlicensed Pro TV & Antena Group Broadcast Content
The site is a fully SEO-optimised WordPress installation using Yoast SEO to generate sitemaps and maximise search engine ranking for Romanian TV show queries. The post sitemap confirms over 500 indexed episode pages updated through September 2026 — daily publishing cadence. The CMS choice, LiteSpeed hosting, and aggressive SEO configuration are consistent with a content farm operator who treats piracy as a traffic acquisition strategy rather than incidental.
The content catalogue is drawn entirely from Romania's two dominant broadcast groups: Pro TV (Las Fierbinți, Românii Au Talent, Power Couple Romania, Survivor Romania) and Antena Group (Mireasa, Chefi la Cuțite, O Nouă Șansă, Asia Express). Both broadcasters hold exclusive digital rights. No licence, no attribution, no takedown mechanism. The "Lumea ta Digitală" ("Your Digital World") branding is the only on-site text.
Reporting Targets
Investigation Method
HTTP check on click-sud.pro confirmed active. DNS lookup returned Cloudflare proxy IPs (104.21.77.124, 172.67.207.173). NS records: ada/cesar.ns.cloudflare.com. IPv6 AAAA records present. Origin IP masked.
WHOIS via whois.com confirmed registration date 2026-01-21, registrar Spaceship Inc., identity fully withheld via WITHHELD FOR PRIVACY LLC (Delaware). Expiry 2027-01-21. One-year registration cycle consistent with domain-cycling operators.
Passive HTTP probe via HackerTarget revealed X-Turbo-Charged-By: LiteSpeed, absent CSP header, absent Set-Cookie. LiteSpeed backend strongly indicates Indian shared hosting. No session cookies from the main domain; all tracking delegated to injected ad JavaScript.
crt.sh query found 12 certificate entries across 6 different CAs (Let's Encrypt R13/E8/YR2/YE1, Google Trust WE1, Sectigo) from May–August 2026. Wildcard *.click-sud.pro issued. Rapid CA rotation is evasion behaviour consistent with bot-protection circumvention.
HTTP follow on clicksud.org revealed 301 chain: clicksud.org → ishtiz.com → taysentotologin.com (Indonesian TOTO gambling portal). WHOIS on ishtiz.com shows domain listed for sale on Sedo, suggesting it was sold or parked as a traffic broker after the operator migrated to click-sud.pro.
HackerTarget pagelinks scrape of click-sud.pro returned 8 external footer links, all .in TLD Android APK distribution sites. Cross-referencing with known malware databases confirmed PikaShow and Dooflix as documented malware vectors. CPI affiliate relationship inferred from consistent .in TLD pattern and lack of any organic editorial link rationale.
ANY.RUN public report for clicksud.biz SHA256 7635a1... confirmed MALICIOUS verdict, 27 indicators, Chrome privacy violation. Sitemap index confirmed WordPress/Yoast SEO CMS, 500+ episode posts from January 2026 through September 17 2026. Content attribution identified Pro TV and Antena Group broadcast material.
| Indicator | Type | Context |
|---|---|---|
| click-sud.pro | domain | Primary active piracy portal, WordPress/LiteSpeed |
| 104.21.77.124 | ip | Cloudflare proxy A record — click-sud.pro |
| 172.67.207.173 | ip | Cloudflare proxy A record — click-sud.pro |
| clicksud.org | domain | Legacy domain — 301 sold to Indonesian gambling chain |
| clicksud.biz | domain | Sister domain — ANY.RUN MALICIOUS verdict |
| ishtiz.com | domain | Traffic broker intermediate hop in gambling redirect chain |
| taysentotologin.com | url | Indonesian illegal TOTO gambling portal — end of clicksud.org chain |
| online.taysentoto-pintu.com | url | Gambling registration endpoint |
| pikashowdl.in | domain | APK partner — PikaShow, documented Android spyware |
| dooflix.org.in | domain | APK partner — Dooflix, adware + data harvesting |
| mt-manager.com.in | domain | APK partner — MT Manager root file manager |
| tekken3.io.in | domain | APK partner — Fake Tekken 3, malware loader |
| tekken3.net.in | domain | APK partner — Fake Tekken 3 variant |
| vn-app.com.in | domain | APK partner — VN Video Editor .in clone |
| anime-world.com.in | domain | APK partner — pirated anime portal |
| wahoproapp.com.in | domain | APK partner — unknown payload |
| cloud.fifu.app | domain | Suspicious tracker (ANY.RUN — clicksud.biz report) |
| cdn.fifu.app | domain | Suspicious CDN (ANY.RUN — clicksud.biz report) |
| 172.67.206.50 | ip | Cloudflare IP — clicksud.biz (ANY.RUN report) |
| 104.21.82.191 | ip | Cloudflare IP — clicksud.biz (ANY.RUN report) |
| 7635a16051f1a70f6147e686e91be88e0765f88589604b75c1787dc4aafc0156 | sha256 | clicksud.biz malicious sample — ANY.RUN report |
| 3C42A05C3C3F1C66543BB9C5ADF5EAEC | hash | clicksud.biz malicious sample — MD5 |
| ada.ns.cloudflare.com | infra | Cloudflare NS — click-sud.pro |
| cesar.ns.cloudflare.com | infra | Cloudflare NS — click-sud.pro |
Evidence — WHOIS & Domain Chain
Evidence — Monetisation Map