Case 003: dulo.cx — Full Stack Exposure of a Streaming Piracy Operation
Passive browser analysis of an unauthorized movie streaming platform — no tools beyond Chrome DevTools and a HAR export. Findings: covert click-fraud tracker on every interaction, their Supabase project URL and anon key in the JS bundle (a public key, so the open question is whether row level security is configured, which was not tested), admin panel routes exposed, self-hosted analytics dashboard publicly accessible, 5 rotating Turnstile keys hardcoded, CORS failures on their own CDN, and zero-consent profiling of anonymous users.
dulo.cx (formerly dulo.gd, branded "Dulo TV") is an unauthorized movie and TV streaming site. A passive investigation using only Chrome DevTools and a HAR export produced a complete technical breakdown of their entire operation — far beyond the core copyright violation.
Clicking anything on dulo.cx does not change the URL bar. This is intentional — the site is a SPA using query-string routing with history.pushState() deliberately disabled, to minimize URL exposure and frustrate DMCA crawlers.
event.preventDefault() on everything. No traditional page loads. The browser never navigates./?info=movie:TMDBIDEvery page interaction fires a silent POST to ay267.com. This is not an ad — it is an affiliate conversion beacon. It runs even when no ad is displayed. The userId is persistent across the entire session and assigned without login, without consent, without a cookie banner.
zoneid=11545831 is dulo.cx's publisher slot — they earn per session tracked. The rb= obfuscated payload is specifically designed to avoid anti-fraud detection. syncOrigin=gidrator is the sub-network routing their traffic. Together: behavioral data from every visitor is sold without their knowledge.
userId and firing conversion events on anonymous users without any consent mechanism violates GDPR Article 6 (lawful basis) and Article 13 (transparency). Confirmed by IndexedDB check — zero auth token present, yet profiling is active from the very first page load.
The JS bundle contains their Supabase project URL and the anon key in plain text, in supabase-G_Sidcym.js, readable by any visitor in DevTools, Sources. This is how Supabase is meant to work. The anon key is a publishable key: it is shipped to every browser on purpose, and what it can actually read or write is decided entirely by row level security policies on the server. So the finding here is not "a secret leaked", it is "the backend is now identified, and whether it is safe depends on configuration we cannot see from outside".
Their analytics runs on Rybbit (open-source, same tool used on SevinHub) hosted at stats.dulo.gd. The login page is publicly reachable with no IP restrictions — only the password protects their full traffic dashboard.
Cloudflare Turnstile is their anti-bot layer. A Turnstile sitekey is public by design: it has to be in the page for the widget to render, and it is useless without the secret key, which stays on their server and was never visible to us. So none of these five is a leaked credential. What is worth noting is that they ship five sitekeys instead of one, which is a rotation set: when one gets blocked they move to the next. All five are readable in plain text in PlayerV2Modal-DUGIKnTl.js.
Chrome console shows 87 errors and 30 warnings — almost all CORS failures from d.dulo.gd, their old-domain video CDN, being rejected by the browser when called from the new domain dulo.cx. A post-migration misconfiguration they haven't fixed.
| Type | Value | Context |
|---|---|---|
| Domain | dulo.cx | Active unauthorized streaming site |
| Domain | dulo.gd | Former domain — still active as CDN origin (d.dulo.gd) |
| Tracker | ay267.com | Covert click-fraud tracker — fires on every interaction without consent |
| Zone ID | 11545831 | dulo.cx's affiliate publisher slot at ay267.com |
| Storage | __BI_SESSION_11545831 | Persistent UUID assigned to all visitors without consent |
| Storage | syncOrigin = gidrator | Affiliate sub-network routing dulo.cx traffic |
| API Key | 0fd8ade0f772180c8f8d651787c35e14 | TMDB API key — hardcoded in JS, abused for commercial piracy |
| Backend | wsudbodtjjfenprwsagd.supabase.co | Supabase project URL — exposed in supabase-G_Sidcym.js |
| Anon Key | eyJhbGc... (JWT) | Supabase publishable key, public by design, listed to identify the project not as a leak |
| Analytics | stats.dulo.gd/login | Self-hosted Rybbit — login publicly accessible, no IP restriction |
| Proxy | vidapi-sabrina-proxy.vidsuper1.workers.dev | Cloudflare Worker video signing proxy |
| Storage | amri-source-worked | Internal codename for video source routing system |
| Endpoint | dulo.cx/api/access-check | Session validator — 30s polling, enforces free-tier limits |
| Admin Routes | /admin /admin/users /admin/content /admin/sources | Full admin route map exposed in JS bundle |
| Turnstile Sitekeys | 5x 0x4AAAAAAA... (in page) | Public sitekeys, not secrets; the full rotation set, all reportable at once |
| CDN Failure | d.dulo.gd CORS (87 errors) | Old-domain CDN not updated — significant video library broken |
EUIPO — EU Intellectual Property Office
Reported dulo.cx for commercial unauthorized streaming. Evidence: domain history, video proxy infrastructure, TMDB API abuse, admin route structure, affiliate monetization proof. EUIPO coordinates with registrars and national IP authorities across EU member states. Contact: infringement@euipo.europa.eu — Online Infringement Reporting Portal.
APD / GBA — Belgian Data Protection Authority
Reported for GDPR violations under Article 6 (lawful basis) and Article 13 (transparency): persistent anonymous profiling via ay267.com, no consent mechanism, no cookie banner, behavioral data sold to affiliate network. APD can impose fines up to 4% global turnover. Contact: contact@apd-gba.be — complaint.apd-gba.be
TMDB — API Key Abuse
Reported key 0fd8ade0f772180c8f8d651787c35e14 for revocation. Removes all metadata, poster images, and search functionality. Contact: api@themoviedb.org — TMDB API Abuse.
Cloudflare — Workers Abuse + Turnstile Key Revocation
Reported vidsuper1.workers.dev for proxying pirated content. Reported all 5 Turnstile sitekeys together, so a rotation strategy that assumes one key at a time has nothing to fall back to if Cloudflare acts on them. Contact: abuse@cloudflare.com — cloudflare.com/abuse/form
FCCU Belgium — Federal Computer Crime Unit
Reported specifically for the unauthorized tracking of Belgian residents: ay267.com installs persistent identifiers on Belgian users' devices without consent from the first page load — this constitutes unauthorized computer-based collection of personal data under Belgian criminal law, separate from the GDPR civil case filed with APD/GBA. Contact: fccu@police.belgium.eu
EC3 / Europol — European Cybercrime Centre
Reported the organized cross-border piracy operation to ec3@europol.europa.eu. The operation's low-cost self-hosted architecture (Rybbit + Supabase + Cloudflare Workers), deliberate DMCA-evasion design, and domain rotation pattern indicate a professional repeat operator. EC3 scope: cross-border IP crime + unauthorized tracking of EU users at scale.
This investigation used only Chrome DevTools. No external tools, no exploitation, no unauthorized access. Every finding was data the site transmitted to the browser or embedded in its own code.
Phase 1 — HAR analysis: Exported the HTTP Archive from the Network tab. Mapped tracker behavior, API endpoints, and video delivery architecture from raw request/response pairs.
Phase 2 — JS bundle analysis: Sources tab → located named JS chunks. Read plain-text source directly in the browser. Extracted hardcoded keys, admin routes, internal codenames, Turnstile keys, and provider tier logic. No decompiler needed.
Phase 3 — Storage forensics: Application tab → confirmed anonymous profiling by verifying absence of auth tokens alongside presence of persistent tracker identifiers in localStorage.
Headless browser screenshot of dulo.cx captured during investigation. Unauthorized streaming site serving copyrighted content while running covert click-fraud tracker, Supabase backend exposure, and zero-consent user profiling.
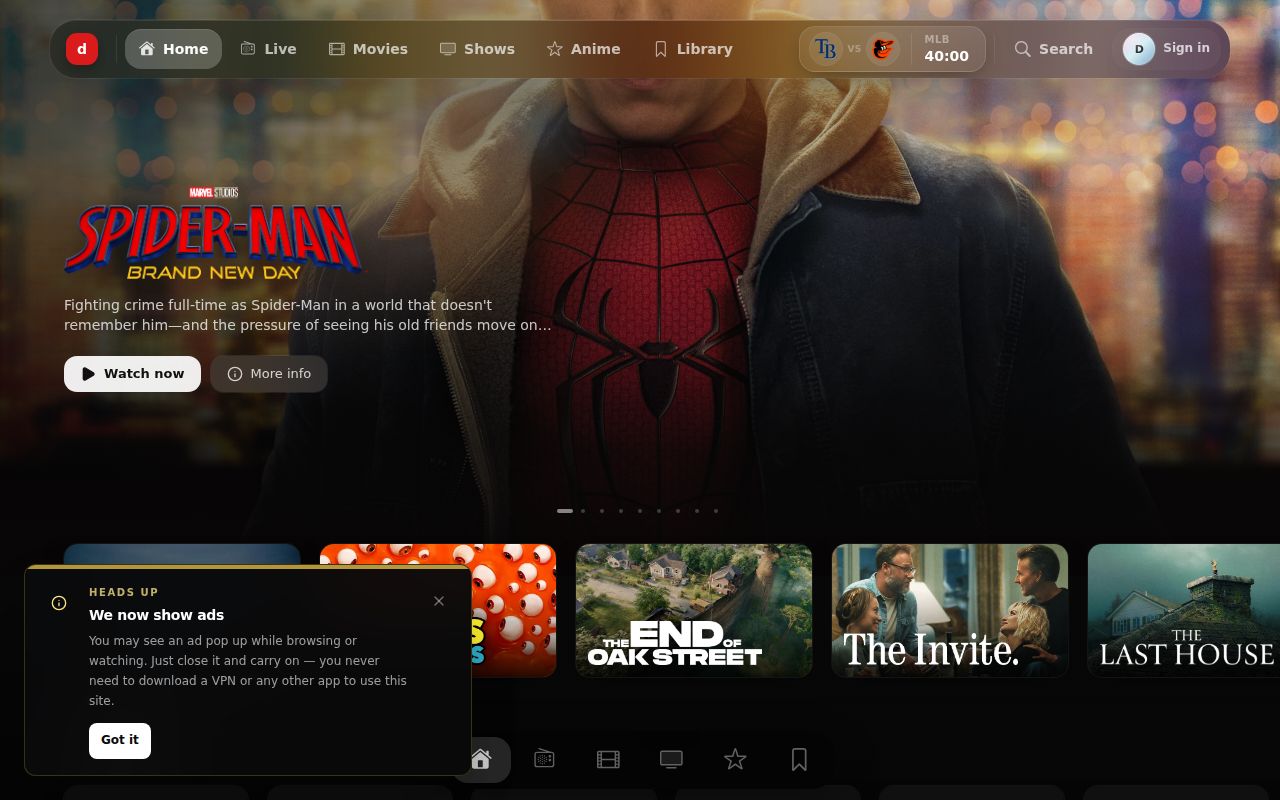
Evidence captured passively. Site has no content licensing, no cookie consent, and runs covert tracking on all visitors.